Connecting AAA to LDAP, HSS and External Identity Stores
Learn how to integrate an AAA server with LDAP and HSS using bind authentication and Diameter SWx, including synchronization, security, failover, and implementation considerations.
Learn how to integrate an AAA server with LDAP and HSS using bind authentication and Diameter SWx, including synchronization, security, failover, and implementation considerations.
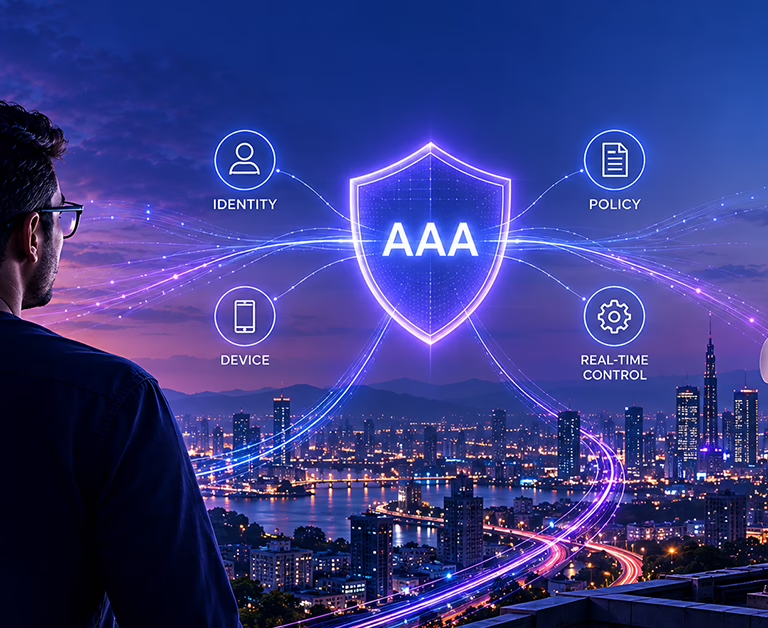
Learn how AAA enables Zero Trust in telecom networks through dynamic policy, continuous verification, session reauthorization, and CoA.
Learn how consolidating multiple AAA systems can reduce operational overhead, simplify compliance, improve subscriber experience, and support a stronger ROI case.
Should you build or buy your AAA stack? Compare costs, protocols, availability, compliance, risks, and engineering effort to make the right decision.
Learn how TACACS+ supports SOC 2 access control evidence, including command accounting, role-based access, monitoring, change management, and audit artifacts.
How to separate real AI detection capability from marketing language when evaluating AAA vendors.
Learn how to troubleshoot common 802.1X authentication failures, including supplicant, certificate, RADIUS, MTU, VLAN, and network issues.
TACACS+ ran for two decades on an expired Internet-Draft with no formal standard behind it. RFC 8907 (IETF, September 2020) documents the protocol as deployed, but as an Informational RFC rather than a Standards Track one, and it describes the protocol’s packet protection as obfuscation, not encryption. RFC 9887 (9 December 2025, Proposed Standard) updates […]
Overview The rest of this cluster asks how you verify a vendor’s reliability claims. This article flips the direction: once your authentication, authorization, and accounting (AAA) platform is reliable, how do you prove it to the regulator who sets the penalties and the enterprise customer who decides whether to renew? Regulators generally want compliance-format reporting: […]
A multi-site AAA server deployment only survives a site loss if five things are executed, not assumed: subscriber and session state replicated across sites in real time and asynchronously to the auth path; every request routed to the nearest healthy site with NAS (network access server) timers set from measured latency; failover drills that isolate […]