How to Reduce AAA Server Deployment Risk

Reducing AAA (authentication, authorization, and accounting) server deployment risk means addressing six recurring failure modes session-state loss, undersized capacity, protocol misconfiguration, incomplete rollback plans, NAS onboarding gaps, and accounting data mismatches each with a specific, testable mitigation applied before cutover. The risk register table below turns those six into a working project artifact you can […]
Read more

Community Broadband Operators: A Lean Systems Stack That Still Scales

Community and municipal broadband operators face a real tension: budgets say start minimal, growth plans say don’t buy anything you’ll outgrow. The way through is a community broadband lean systems stack, core Authentication, Authorization, and Accounting (AAA) and billing only at launch, chosen on scale-ready architecture rather than feature count. Prioritize subscriber authentication, usage accounting, […]

Read more

AAA Server Rollout Strategies for Telecom Operators

AAA server rollout strategies fall into three models, big-bang (fast, higher risk), phased by subscriber segment (slower, lower risk), and parallel-run (old and new authentication, authorization, and accounting platforms live simultaneously, lowest risk) chosen based on operator scale, network complexity, and risk tolerance. Most large operators combine models, sequencing them differently per network type. Most […]

Read more

AAA Server Installation Checklist

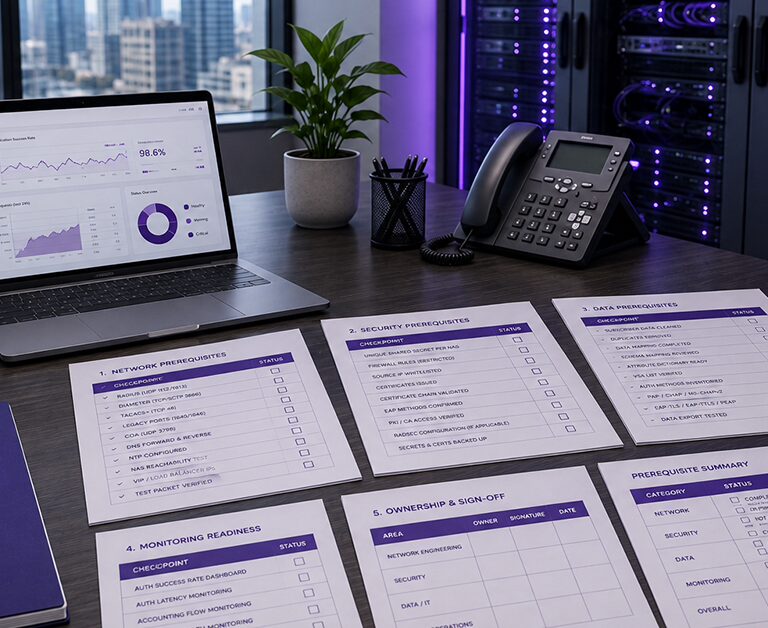
An AAA (authentication, authorization, and accounting) server installation checklist covers four categories of prerequisites that decide whether install week runs clean: network (verified port paths, DNS, NTP), security (unique shared secrets per NAS, scoped firewall rules, certificates), data (a cleaned subscriber extract mapped to the new schema), and monitoring (dashboards and alerting live before the […]

Read more
AAA Server Modernization Business Case: Buyer's Framework

AAA Server Modernization Business Case: Buyer’s Framework

The hardest part of modernizing AAA (Authentication, Authorization, and Accounting) infrastructure is rarely the engineering. It is the meeting where finance asks why the company should spend real money on a system that, as far as anyone in the room can tell, works. “Our RADIUS server is old” is a true statement and a losing […]

Read more
How to Compare AAA Server Architectures

How to Compare AAA Server Architectures

To compare AAA server architectures, score six structural choices: redundancy model, protocol convergence, session and data model, scaling approach, deployment flexibility, and operational tooling. These decide how an AAA (Authentication, Authorization, and Accounting) platform behaves under load and during failure. The vendor diagram does not. Redundancy model and data model dominate the outcome. Active-active sites […]

Read more
Selecting an AAA Server for Long-Term Network Growth

Selecting an AAA Server for Long-Term Network Growth

Most Authentication, Authorization, and Accounting (AAA) procurement goes wrong the same way: the evaluation tests what each vendor supports today against the traffic the network carries today. Both numbers are about to change. Subscriber counts grow, a fiber footprint expands into a second region, a deal with a Mobile Virtual Network Operator (MVNO) adds Diameter […]

Read more
6 Signs Your Current AAA Server Needs an Upgrade

6 Signs Your Current AAA Server Needs an Upgrade

Nobody schedules a meeting to discuss whether the Authentication, Authorization, and Accounting (AAA) server is fine. The platform authenticates every session, the dashboards are green enough, and attention goes elsewhere. Then the evening peak produces a spike in RADIUS authentication timeouts, a vendor email announces an end-of-support date, or a new requirement arrives in a […]

Read more
How TACACS+ Compares to RADIUS for Network Authentication

How TACACS+ Compares to RADIUS for Network Authentication

Overview RADIUS vs TACACS+ is not a contest with a winner; the two protocols answer different questions. RADIUS decides who may use the network – subscribers, devices, Wi-Fi clients – over UDP at very high volume. TACACS+ decides who may administer the network – engineers logging in to routers, switches, and firewalls – over TCP, […]

Read more

Subscribe to our Newsletter

Receive the latest news

Subscribe To Our Newsletter