TLDR
What port does RADIUS use?
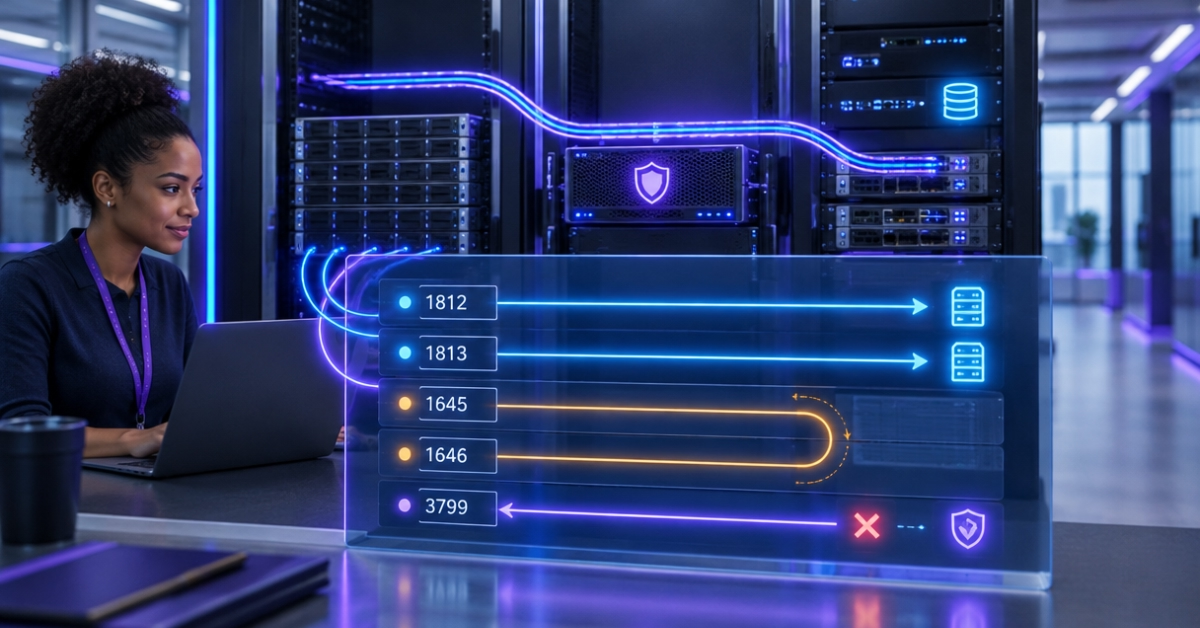
- The RADIUS port for authentication is UDP 1812 (RFC 2865 §3); accounting uses UDP 1813 (RFC 2866 §3).
- 1645 and 1646 are the pre-standard pair; RFC 2058 and RFC 2059 (January 1997) already used 1812 and 1813.
- Change of Authorization (CoA) and Disconnect requests go to the network access server (NAS) on UDP 3799 (RFC 5176 §2.1).
- RadSec uses TCP 2083 (RFC 6614 §2.1); a July 2026 Internet Engineering Task Force (IETF) draft would bar RADIUS/UDP outside secure networks.
RADIUS uses UDP port 1812 for authentication and authorization and UDP port 1813 for accounting, as assigned by IANA and defined in RFC 2865 and RFC 2866. Older equipment may still use ports 1645 and 1646. Change-of-Authorization and Disconnect messages use UDP port 3799 (RFC 5176), and RADIUS over TLS (RadSec) uses TCP port 2083 (RFC 6614).
This guide is for network operations center (NOC) engineers, architects and security engineers at Internet Service Providers (ISPs), carriers, wireless ISPs and cable operators. There, the Remote Authentication Dial-In User Service (RADIUS) client is a broadband network gateway (BNG), broadband remote access server (BRAS), wireless LAN controller (WLC) or cable modem termination system (CMTS). It talks to an authentication, authorization and accounting (AAA) server; for packet basics, see how the RADIUS protocol works.
The five RADIUS ports at a glance
Each standard RADIUS port number has an RFC and an Internet Assigned Numbers Authority (IANA) registry entry. Every port has one job; when a firewall request fails, check direction first.
| Port | Transport | Sent by → to | Defined in | Carries | If blocked |
| 1812 | UDP | NAS → AAA server | RFC 2865 §3; IANA “radius” | Access-Request; Accept, Reject, Challenge | Logins fail once retries and failover run out |
| 1813 | UDP | NAS → accounting server | RFC 2866 §3; IANA “radius-acct” | Accounting-Request; Accounting-Response | No usage records reach billing |
| 1645 | UDP | NAS → AAA server (legacy) | Pre-standard; RFC 2865 Implementation Note | Same as 1812 | Legacy NAS logins fail |
| 1646 | UDP | NAS → accounting server (legacy) | Pre-standard; RFC 2866 Implementation Note | Same as 1813 | Legacy NAS accounting lost |
| 3799 | UDP | AAA or policy server → NAS | RFC 5176 §2.1; IANA “radius-dynauth” | CoA-Request, Disconnect-Request; ACK/NAK | CoA and disconnects silently dropped |
Set 1812 and 1813 on both the NAS and the AAA server; they are the RADIUS default ports (RFC 2865 §3, RFC 2866 §3). Device administration uses TACACS+ port 49 over TCP instead (RFC 8907 §3.4).
Port 1812 and 1813: authentication and accounting
Which port does RADIUS authentication use? UDP 1812; accounting uses UDP 1813. The NAS opens both, and the server replies with the ports reversed (RFC 2865 §3, RFC 2866 §3).
What travels on port 1812 and port 1813
On 1812 the NAS sends an Access-Request and the server returns an Access-Accept, Access-Reject or Access-Challenge (RFC 2865 §4). The Access-Accept carries the authorization, such as an IP pool or rate limit.
Port 1813 carries Accounting-Request packets: a Start, periodic Interim-Updates (RFC 2869 §2.1) and a Stop (RFC 2866 §5.1), each answered by an Accounting-Response.

The five RADIUS ports at a glance: Mobile-core AAA links such as SWm (ePDG to 3GPP AAA server) use Diameter on port 3868 (RFC 6733 §2.1), not RADIUS.
Does RADIUS accounting use a different port?
Yes, port 1813. Authentication is latency-sensitive, while accounting is volume-heavy. The NAS resends each Accounting-Request until answered, and the server must not answer before the record is stored (RFC 2866 §2).
Separate ports let operators scale and filter each flow.
Ports 1645 and 1646: the legacy pair and why they still appear
Port 1645 and port 1646 carry the same packets as 1812 and 1813 (RFC 2865 §3, RFC 2866 §3). RADIUS works on any port both ends agree on, so the RADIUS port 1812 vs 1645 question keeps coming up.
The 1997 reassignment
Early deployments used 1645 and 1646, numbers IANA had already registered to “datametrics” and “sa-msg-port” (RFC 2865 and RFC 2866 Implementation Notes). The first RADIUS RFCs, 2058 and 2059 (January 1997), already used 1812 and 1813. RFC 6613 §2.2 also bars the old pair as TCP defaults.
Handling NAS equipment that still defaults to 1645 and 1646
Some NAS firmware still defaults to the legacy pair. Move the NAS to 1812 and 1813 (RFC 2865, 2866), let the AAA server listen on both pairs during cut-over, then close the old pair.
Port 3799: CoA and Disconnect, the port most firewalls forget
Port 3799 is the RADIUS CoA port, registered with IANA as “radius-dynauth” and specified by RFC 5176 §2.3; its traffic runs the other way. The AAA or policy server, the Dynamic Authorization Client (DAC), sends a CoA-Request or Disconnect-Request to port 3799 on the NAS. The NAS answers ACK or NAK (RFC 5176 §2.1 to §2.3).
Operators use it to change live sessions, such as redirecting a prepaid subscriber out of quota; see our guide to Change of Authorization.
In new deployments, 3799 is the port we most often find blocked. Rules written for 1812 and 1813 assume the NAS starts every exchange, so the stateful firewall has no session to match and drops the CoA-Request.
Authentication and accounting keep working, so nobody notices until a policy change fails to reach the NAS. Stateless filters must also pass the ACK or NAK back, and a NAS behind NAT needs a static mapping for 3799.
Some NAS firmware still expects CoA on UDP 1700, a legacy vendor default no RFC assigns. Move it to 3799 (RFC 5176 §2.1).
UDP vs TCP vs TLS: how RADIUS transport is changing
Does RADIUS use TCP or UDP? UDP, on every port above. A RADIUS TCP port exists on the same numbers (RFC 6613 §2.2), and the IETF is pushing operators toward TLS.
| Transport | Port | Defined in | Status (November 2026) | Protection |
| RADIUS/UDP | UDP 1812, 1813, 3799 | RFC 2865 §3, 2866 §3, 5176 §2.1 | Default; deprecation drafted | Shared secret, MD5; Message-Authenticator (RFC 2869 §5.14) |
| RADIUS/TCP | TCP 1812, 1813, 3799 | RFC 6613 §2.2 | Experimental; TLS or IPsec only | None of its own |
| RADIUS/TLS (RadSec) | TCP 2083 | RFC 6614 §2.1 | Experimental; successor pending | TLS |
| RADIUS/DTLS (RadSec) | UDP 2083 | RFC 7360 §3.1 | Experimental; same successor | Datagram TLS (DTLS) |
Why does RADIUS use UDP?
Per RFC 2865 §2.4, a client must fail over to a secondary server quickly, so it keeps each request and runs its own timers; TCP adds little. Each UDP datagram carries one RADIUS packet (RFC 2865 §3).
Retransmissions keep the same Identifier, Request Authenticator and source port (RFC 2865 §2.5), with jitter and backoff from RFC 5080 §2.2.1. The server spots duplicates by source address, port and Identifier (RFC 2865 §3) and answers them from a reply cache (RFC 5080 §2.2.2).
That cache keeps a carrier-grade AAA steady when thousands of subscribers reconnect after an outage; a server that falls behind triggers more retries and failover. The Alepo AAA Server datasheet rates the platform at 36,000+ transactions per second with sub-millisecond latency.
# Illustrative NAS log: RFC 5080 default timers, documentation addresses
t=0.0s Access-Request id=142 -> 192.0.2.11:1812 user=sub-****8841 sport=50114
t=2.1s no reply; retransmit #1 id=142 sport=50114 (same Request Authenticator)
t=6.2s no reply; retransmit #2 id=142 sport=50114
t=14.2s no reply; retransmit #3 id=142 sport=50114
t=30.0s 192.0.2.11 marked unreachable; failing over
t=30.0s Access-Request id=142 -> 192.0.2.12:1812
t=30.011s Access-Accept id=142 <- 192.0.2.12 (11 ms)
RADIUS/TCP
Can RADIUS run over TCP? Yes: RFC 6613 (Experimental, 2012) defines it on TCP 1812, 1813 and 3799 (§2.2), but only inside TLS, IPsec or another secure layer (§1). A NAS should stay on UDP (§1.1), and the deprecation draft below marks RADIUS/TCP NOT RECOMMENDED (§6.1).
RadSec on port 2083 and the UDP deprecation
RADIUS port 2083 is registered to RadSec: TLS over TCP (RFC 6614 §2.1) and DTLS over UDP (RFC 7360 §3.1). One port carries authentication, accounting and dynamic authorization. Its standards-track successor, draft-ietf-radext-radiusdtls-bis-18, is in IESG evaluation and not yet an RFC.
CVE-2024-3596 (BlastRADIUS), disclosed July 9, 2024, added urgency to work already under way. An on-path attacker can turn, for example, an Access-Reject into an Access-Accept by forging the MD5-based Response Authenticator on RADIUS without TLS.
The IETF’s draft-ietf-radext-deprecating-radius-10 (July 3, 2026, still a draft) would bar RADIUS/UDP and RADIUS/TCP outside secure networks (§3.1) and require RadSec or IPsec there (§3.2). Where UDP remains, it would require Message-Authenticator in every Access-Request (§4.2) and first in every reply to one (§4.5).
Our RADIUS security guide covers shared secrets, Message-Authenticator and the BlastRADIUS fix.
Which RADIUS ports to open on a firewall, and where
Write each rule in the direction the exchange starts and let connection state carry the replies. If a request form asks “RADIUS port: TCP or UDP?”, answer UDP for 1812, 1813 and 3799 (RFC 2865, 2866, 5176). RadSec needs TCP 2083 (RFC 6614 §2.1), or UDP 2083 for RADIUS/DTLS (RFC 7360 §3.1).
# Vendor-neutral stateful rule set
# NAS_NETS = BNG/BRAS, WLC and CMTS source addresses
# AAA_SERVERS = authentication, accounting and policy (DAC) hosts
# PEER_AAA = roaming or wholesale partners’ AAA servers, if you proxy
# Replies are permitted by connection state, not by extra rules.
# NAS starts these exchanges
permit udp from NAS_NETS to AAA_SERVERS port 1812 # Access-Request (RFC 2865)
permit udp from NAS_NETS to AAA_SERVERS port 1813 # Accounting-Request (RFC 2866)
# AAA or policy server starts these exchanges
permit udp from AAA_SERVERS to NAS_NETS port 3799 # CoA-/Disconnect-Request (RFC 5176)
# permit udp from AAA_SERVERS to NAS_NETS port 1700 # legacy CoA default, only if unavoidable
# RadSec, only where enabled
permit tcp from NAS_NETS to AAA_SERVERS port 2083 # RADIUS/TLS (RFC 6614)
# permit udp from NAS_NETS to AAA_SERVERS port 2083 # RADIUS/DTLS (RFC 7360), if used
# If CoA also moves to RadSec, add AAA_SERVERS -> NAS_NETS tcp 2083 (RFC 6614 §2.1: one port)
# Proxy peers: RadSec only across partner links (deprecation draft §3.2)
permit tcp from AAA_SERVERS to PEER_AAA port 2083 # we proxy to a home AAA (RFC 6614)
permit tcp from PEER_AAA to AAA_SERVERS port 2083 # partners proxy to us (RFC 6614)
# Legacy pair: temporary, remove after migration
# permit udp from NAS_NETS to AAA_SERVERS port 1645,1646
deny udp from any to AAA_SERVERS port 1812,1813,1645,1646 log
Worked example: a regional ISP adds a new BNG
A regional ISP adds a BNG at a remote site; its AAA and policy servers sit in two data centers behind a stateful firewall.
- Permit UDP 1812 and 1813 (RFC 2865, 2866) from the BNG to both AAA sites, so failover has somewhere to go.
- Permit UDP 3799 (RFC 5176) from the policy servers to the BNG, since CoA and Disconnect-Request start there.
- Give the BNG its own shared secret. The server picks the secret by source IP (RFC 2865 §3), so any NAT must keep that address stable.
- Before go-live, test an authentication, an accounting Start and Stop, and a Disconnect-Request.
- If the firmware defaults to 1645 and 1646, or to 1700 for CoA, change the BNG rather than opening those ports.
Frequently asked questions
Q1. Is RADIUS TCP or UDP?
UDP by default, on 1812, 1813 and 3799 (RFC 2865, 2866, 5176). RADIUS/TCP (RFC 6613) runs only inside TLS or IPsec, and RadSec uses TCP 2083 (RFC 6614 §2.1).
Q2. What is port 1812 used for?
RADIUS authentication and authorization: the NAS sends Access-Requests and gets an Access-Accept, Access-Reject or Access-Challenge back (RFC 2865 §3 and §4).
Q3. What is port 1813 used for?
RADIUS accounting: the NAS sends Start, Interim-Update and Stop records and retries until an Accounting-Response arrives (RFC 2866 §2 and §3).
Q4. Why does RADIUS have ports 1645 and 1646?
Early implementations chose them before the first RADIUS RFCs, clashing with services IANA had already registered. RFC 2058 and RFC 2059 (January 1997) used 1812 and 1813.
Q5. What port does RADIUS CoA use?
UDP 3799 (RFC 5176 §2.3), for CoA-Request and Disconnect-Request. The AAA or policy server sends them, so the firewall needs a rule toward the NAS.
Q6. What port does RadSec use?
TCP 2083 for RADIUS/TLS (RFC 6614 §2.3) and UDP 2083 for RADIUS/DTLS (RFC 7360 §3.1), one port for all RADIUS traffic.
Q7. Do I need to open RADIUS ports in both directions?
On a stateful firewall you need one rule per initiating direction: NAS to AAA for 1812 and 1813, AAA to NAS for 3799 (RFC 5176 §2.1). Stateless filters must also permit replies (RFC 2865 §3).
Q8. Which RADIUS port does Wi-Fi authentication use?
The RADIUS port for Wi-Fi authentication is UDP 1812, with 1813 for accounting (RFC 2865, 2866). The WLC or access point is the NAS; it relays the EAP exchange from 802.1X inside RADIUS EAP-Message attributes (RFC 3579 §2.1).
Conclusion
Many RADIUS port problems trace back to direction: the NAS opens 1812 and 1813, the AAA server opens 3799 (RFC 2865, 2866, 5176). The IETF’s July 2026 draft would take RADIUS off UDP outside secure networks. Enforce Message-Authenticator now (RFC 2869 §5.14) and plan RadSec on TCP 2083 (RFC 6614).