TLDR
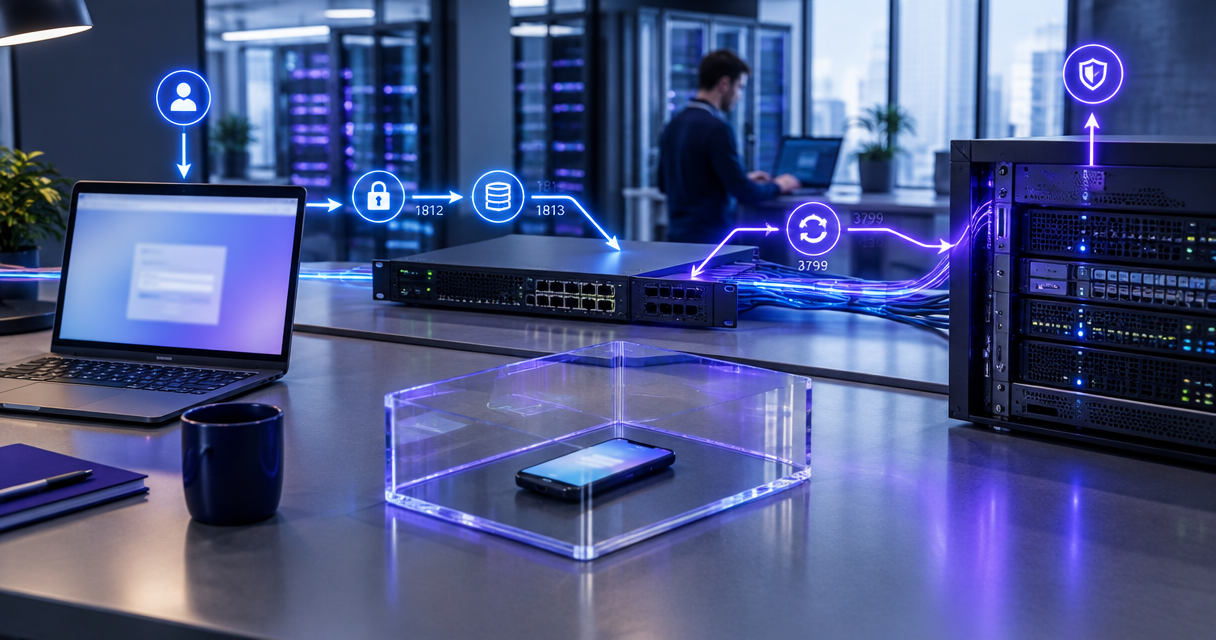
- The NAS keeps a new device in a walled garden of pre-login sites and redirects it to the portal.
- In the NAS-initiated model, the NAS sends the Access-Request after login (RFC 2865, Section 4.1).
- In the CoA model, the AAA server lifts the restriction with a CoA-Request to the NAS on User Datagram Protocol (UDP) port 3799 (RFC 5176, Section 2.3).
- Either way, the NAS tracks the session in Accounting-Request records (RFC 2866, Section 5.1).
In a RADIUS portal flow, the controller or access point (the network access server, or NAS) redirects a new device to the captive portal. After login, either the NAS sends the user’s credentials to the AAA server in an Access-Request, or the AAA server sends a Change of Authorization (CoA) to lift restrictions. Accounting then tracks the session.
AAA means authentication, authorization and accounting. The AAA server talks to the NAS in RADIUS (Remote Authentication Dial In User Service), defined in Request for Comments (RFC) 2865. For the basics, see our guide captive portals and what an AAA server is.
The three parties in a captive portal RADIUS flow
In a captive portal RADIUS flow, the NAS enforces the walled garden, the portal collects the login and the AAA server decides what the session may do. RFC 8952 calls the first two the Enforcement Device and the User Portal (Section 1.2).
The NAS is the wireless LAN controller (WLC), access point or gateway carrying the user’s traffic. Before login, its walled garden reaches only the portal, DNS (Domain Name System) and a short list of other hosts, such as the certificate-check servers in RFC 8952 (Section 2.1). The NAS redirects the device’s first web request to the portal, often adding the client MAC (media access control) address to the URL.
An external captive portal is a separate web server that shows the login, voucher or payment page. Behind it, the AAA server checks credentials, returns policy and stores accounting records over UDP 1812 and 1813 (RFC 2865, Section 3; RFC 2866, Section 3). For the packet format, see how the RADIUS protocol works.
Model 1: NAS-initiated login from an external captive portal
In this model the portal only collects credentials, and the NAS, often a WLC, runs the RADIUS exchange itself. Any NAS with standard RADIUS support can work this way.
External portal RADIUS flow, step by step
- The NAS places the new device in the walled garden and redirects its first HTTP request to the portal.
- The user signs in, and the portal page posts the credentials to the NAS login URL.
- The NAS sends an Access-Request with User-Name, User-Password and Calling-Station-Id (RFC 2865, Section 4.1).
- The AAA server returns an Access-Accept with Session-Timeout and Idle-Timeout, or an Access-Reject (Sections 4.2 and 4.3).
- The NAS lifts the walled garden and sends an Accounting-Request with Acct-Status-Type Start (RFC 2866, Section 5.1).
The browser carries the password to the NAS, so the NAS login page needs HTTPS. On the hop from NAS to AAA server, User-Password is only hidden by an MD5 operation keyed by the shared secret (RFC 2865, Section 5.2), so keep that link on a protected network. Because the NAS always asks first, mid-session top-ups and forced logouts still need a CoA path, which Model 2 provides.
Model 2: captive portal and CoA re-authorization
A CoA-Request (RADIUS code 43, RFC 5176) lets the AAA server change a live session without waiting for the NAS to ask. Here the AAA server meets the device before login, and the portal reports straight to it.
CoA re-authorization flow, step by step
- The NAS sends an Access-Request for MAC authentication, with the device MAC in Calling-Station-Id (RFC 3580, Section 3.21) and an Acct-Session-Id (RFC 5176, Section 3).
- The AAA server returns an Access-Accept with a walled-garden policy and the redirect URL in a Vendor-Specific Attribute (RFC 2865, Section 5.26).
- The user logs in on the portal, which reports the result to the AAA server.
- The AAA server sends a CoA-Request to the NAS on UDP 3799, naming the session by Calling-Station-Id and Acct-Session-Id (RFC 5176, Sections 2.3 and 3).
- The NAS replies CoA-ACK and applies the new policy, or CoA-NAK with an Error-Cause (Section 3.5).
The CoA-Request can carry new policy, such as a Filter-Id that replaces the current one (RFC 5176, Section 3.6, Note 3). It can also carry Service-Type “Authorize Only” with a State attribute, in which case the NAS re-authorizes with a fresh Access-Request (Sections 3.2 and 3.3). The odd part is the reply: the NAS must answer that form with a CoA-NAK carrying Error-Cause 507 (Request Initiated), so here the NAK means success.
In deployments we see, a stalled captive portal CoA login usually means the NAS silently dropped the CoA-Request, as RFC 5176 requires for untrusted sources (Section 6.1). Check the NAS’s CoA client entry for the AAA server, the shared secret, and UDP 3799 on every firewall. Our RADIUS CoA article explains the message types and Error-Cause values.
Because the AAA server sees the MAC address at step 1, it can let a returning device skip the portal. Expire this captive portal MAC caching with the plan, because another device can copy a MAC address and RFC 8952 (Section 3.2.2) asks for identifiers that are hard to spoof.
NAS-initiated vs CoA-initiated hand-off
| Model 1: NAS-initiated | Model 2: CoA-initiated | |
| Message that lifts the walled garden | Access-Accept (RFC 2865, Section 4.2) | CoA-Request (RFC 5176, Section 2.2) |
| Network paths | NAS to AAA server on UDP 1812 and 1813 | Also AAA server to NAS on UDP 3799 |
| Returning devices | Log in again unless the NAS remembers them | Can skip the portal through MAC caching |
Captive portal RADIUS attributes and accounting
In both models, Calling-Station-Id (attribute 31) carries the device MAC address, so the portal, NAS and AAA server agree on which device owns a session. Model 2 adds session identifiers for its CoA-Requests.
| Attribute (type) | Defined in | Model 1 use | Model 2 use |
| User-Name (1) | RFC 2865, §5.1 | Portal login name | Often the MAC address, then the login name |
| Calling-Station-Id (31) | RFC 2865, §5.31; RFC 3580, §3.21 | Device MAC address | Device MAC address; also names the session in CoA |
| Vendor-Specific (26) | RFC 2865, §5.26 | NAS-specific policy | Redirect URL and walled-garden policy |
| Filter-Id (11) | RFC 2865, §5.11 | Post-login policy in Access-Accept | Post-login policy in CoA-Request |
| Session-Timeout (27) | RFC 2865, §5.27 | Maximum session length | Same; a CoA can replace it |
| Acct-Session-Id (44) | RFC 2866, §5.5 | Links accounting records | Also names the session in CoA |
Captive portal accounting
The NAS reports each session on UDP 1813 in Accounting-Request Start, Interim-Update and Stop records (RFC 2866, Section 5.1; RFC 2869, Section 2.1). Each record carries Acct-Session-Id plus running totals such as Acct-Input-Octets and Acct-Session-Time (RFC 2866, Sections 5.3 and 5.7).
The AAA server sets the interim rate with Acct-Interim-Interval: at least 60 seconds, and preferably 600 or more (RFC 2869, Section 5.16). Sessions past about 4.3 GB also need the Gigawords counters (Sections 5.1 and 5.2). In the CoA model, check whether Start goes out at association or after the CoA, since that decides whether walled-garden time counts.
How a captive portal session ends
The Stop record’s Acct-Terminate-Cause gives the reason, such as 5 for Session-Timeout or 4 for Idle-Timeout (RFC 2866, Section 5.10). To end a session early, the AAA server sends a Disconnect-Request to UDP 3799 (RFC 5176, Section 2.1).
Take a WISP (wireless internet service provider) selling one-hour stadium passes. After payment, the CoA-Request carries the full-access Filter-Id and a Session-Timeout of 3600 seconds, and the NAS sends Stop with cause 5 when it expires. NAS platforms differ on whether that timer runs from association or from the CoA, so test it before selling timed passes.
FAQs
Q1. How does a captive portal use RADIUS?
The portal runs the web login, and RADIUS runs between the NAS and the AAA server. Access opens on an Access-Accept or a CoA-Request, and RADIUS accounting records the session.
Q2. Who sends the Access-Request in a captive portal flow?
The NAS: after portal login in the NAS-initiated model, or at association for MAC authentication in the CoA model, where a CoA can trigger a second one (RFC 5176, Section 3.2).
Q3. What does CoA do in a captive portal?
It lets the AAA server change a live session. After login, a CoA-Request on UDP 3799 lifts the walled garden with new policy or a re-authorization request (RFC 5176, Section 2.3).
Q4. How does a captive portal session end?
Session-Timeout or Idle-Timeout expires, the user logs out, or the AAA server sends a Disconnect-Request (RFC 5176, Section 2.1). The Stop record’s Acct-Terminate-Cause shows which (RFC 2866, Section 5.10).
Q5. Which RADIUS attributes carry captive portal data?
The main ones are User-Name, Calling-Station-Id (the device MAC address), Session-Timeout, Idle-Timeout, Filter-Id and Acct-Session-Id. The redirect URL usually travels in a Vendor-Specific Attribute (RFC 2865, Section 5.26).
Q6. How is captive portal usage accounted?
The NAS sends Accounting-Request Start, Interim-Update and Stop records on UDP 1813 (RFC 2866, Section 5.1), at a rate the AAA server sets with Acct-Interim-Interval (RFC 2869, Section 5.16).
Q7. How does MAC caching let returning devices skip the portal?
The AAA server remembers a device’s MAC address after its first portal login, so its next MAC authentication Access-Request gets full access without a redirect.
Conclusion: choosing a hand-off model
Use the NAS-initiated model when the NAS cannot accept CoA-Requests or the AAA server cannot reach it. Use the CoA model when the portal sells time or data or returning devices should skip it, and open UDP 3799 to every NAS before launch.
In any RADIUS portal design, the AAA server makes every access decision. Alepo’s carrier-grade AAA server supports RFC 5176 dynamic authorization alongside real-time policy control and quota management. The AAA Server datasheet lists capacity of 36,000+ transactions per second.
Book a demo to walk through your portal, NAS and AAA hand-off with Alepo’s AAA team.
Running paid or sponsored Wi-Fi? View WiFi Monetization.